

BLOG
Insights on building trust infrastructure for global money movement

Notabene Provides Trust Infrastructure to Support Distributors of Anchorpoint's HKDAP Stablecoin
Supporting Travel Rule-compliant, on-chain settlement as HKDAP's institutional rollout expands into cross-border payments and tokenised asset settlement
Hong Kong, 8 October 2026 – Notabene, the trust layer for global money movement, today announced it is providing Travel Rule compliance and transaction authorisation infrastructure to support authorised distributors of HKDAP ("HKD At Par"), the regulated Hong Kong Dollar-backed stablecoin issued by Anchorpoint Financial Limited ("Anchorpoint"), a Hong Kong-licensed stablecoin issuer. HKDAP is designed to support secure, efficient and compliant digital value transfers across payments, treasury and tokenised asset ecosystems.
HKDAP has entered its Beta Access in August 2026, with Anchorpoint's authorised distributors, including regulated financial institutions and licensed virtual asset exchanges, handling subscription, redemption, and fiat conversion for institutions, corporates, and professional investors. Given that HKDAP settles on a public blockchain network, distributors are subject to Travel Rule obligations requiring counterparty verification and pre-transaction compliance checks as adoption extends into cross border payments and the settlement of tokenised real-world assets. Notabene's enterprise grade transaction authorisation platform automates this Travel Rule compliance, giving distributing institutions real time counterparty verification and pre transaction authorisation before any transfer settles, applying the same trust standards regulated institutions already rely on for traditional cross-border payments.
Notabene's network connects thousands of trusted counterparties across over 100 jurisdictions, giving Anchorpoint's HKDAP authorised distributors immediate, Travel Rule-compliant counterparty reach and enabling connections of institutional clients without building bilateral compliance connections on a one-to-one basis.
To support HKDAP ecosystem, Notabene offers authorised distributors that join its network a dedicated onboarding and support team, and regional data residency options for institutions with data sovereignty requirements. The aim is to help distributors demonstrate to institutional clients their readiness to meet Travel Rule obligations, while bringing key counterparties onto the same open network of thousands of regulated institutions. Each distributor and counterparty that connects makes the network more useful for the next, extending compliant reach across the market.
"Financial institutions distributing HKDAP expect a stablecoin transfer to meet the same standard as a wire: you know who is on the other side before the money moves. We're putting dedicated teams and regional infrastructure behind Anchorpoint's authorised distributors so that check happens in real time and never slows a payment down. That's what it takes for HKDAP to be used for cross-border settlement at an institutional scale."
—Daniel Nicolas, VP of Global Sales at Notabene
"Trust is the foundation of every financial network. Technology can make transactions faster, but sustainable commercial growth happens when institutions have confidence in the people, standards and safeguards behind every interaction. With Notabene bringing its global capabilities and network to the region, this strengthens the infrastructure needed for the next phase of digital finance and reinforces Hong Kong's role as a leading gateway between traditional and digital economies,"
—Milton Lam, Chief Commercial Officer & Co-Founder of Anchorpoint
About Anchorpoint
Anchorpoint Financial Limited is a subsidiary of Standard Chartered Bank (Hong Kong) Limited (SCBHK) and a joint venture established by SCBHK, HKT, and Animoca Brands in February 2025. With the vision of utilising tokenised money to rewire and supplement existing financial infrastructure for the betterment of the real economy, the initial goal is to build and advance the regulated HKD stablecoin “HKDAP” to serve as a secure tokenised medium of exchange for digital economy and to facilitate international payments and capital flows. It is one of the first entities granted with a stablecoin issuer licence (licence number FRS01) by the Hong Kong Monetary Authority under the Stablecoins Ordinance in April 2026.
For further information, please visit our Website and follow us on LinkedIn. For media enquiry please reach out at [email protected]
About Notabene
Notabene is the trust layer for global money movement. The Notabene network connects thousands of trusted counterparties, facilitating trillions of dollars in transaction volume annually across over 100 jurisdictions. Notabene provides industry leading tools for stablecoin payment coordination, real-time transaction authorization, counterparty verification, and self-hosted wallet identification, helping institutions build trust into every transaction.
Media Contact:
Clay Fain
VP Marketing, Notabene
I’ve now spent over 20 years in AML, and the first question I keep getting is: Who decided to send this money?
Last week at Sibos in Miami, Fed Governor Christopher Waller asked the same question to a room full of bankers:
"Who is on the hook if an agent makes the wrong purchase?"
I haven't stopped thinking about his question since.
Funny enough, at a client dinner the same night, the table's verdict on Sibos was pretty blunt in that every panel sounded the same. The ongoing keywords of payments, tokenization, stablecoins, AI, and repeat. Buried in all the sameness was the question I think matters most for anyone in compliance.
Gov. Waller split agentic commerce into two models: Agent-assisted, where you stay in control and agent-delegated, where the buyer "grants authority to an AI agent to shop and make payments on their behalf." He expects consumer shopping to go first and B2B to follow, and he named the catch himself: "higher transaction values typical in B2B commerce amplify the financial exposure from agent errors."
In other words, for my compliance colleagues: larger transaction values, accelerated decision-making, and zero manual sign-off.
And the Sibos program already had the next step on the agenda. One session in the Securities and FX stream is called "AI as market agent and counterparty." The keyword here is “counterparty.” We're not talking about a chatbot helping someone fill out a form anymore.
Call it Know Your Agent (KYA), the agent-era version of KYC: who the agent acts for, what the agent is allowed to do, and how you shut it off.
We already know how to do this. Sort of.
Banks have handled "someone acting for someone else" for a long time. When a company wires $5 million, nobody checks only the company. You check the signatory list, the board resolution, the limit on each signer, the power of attorney, any standing instructions, etc. Authority has a paper trail, and every ops team knows where the paper lives.
The problem is the paper. An agent needs the same trail, in a format a machine reads before the payment moves, and one the counterparty on the other side sees too.
Six know your agent (KYA) questions for compliance teams
Six questions I'd put to any compliance team rolling out (or receiving) agent payments:
Who is the principal? Our CDD covers the person or the business. The agent's mandate sits outside the file.
What is the agent allowed to do? Limits, payees, assets, jurisdictions, an end date. Where do those rules live? Does the other side ever see them? And when both sides run agents, whose rules win?
Whose instruction is this? FATF's revised Recommendation 16 says the payment chain starts "with the financial institution which receives an instruction from the customer." Okay. A human sets a goal. The agent picks the payee, the amount, the timing and the rail. Which part was the instruction?
Who owns the sanctions hit? OFAC's own Sanctions Compliance Guidance for the Virtual Currency Industry (October 2021) spells out the rule: civil penalties apply on "a strict liability legal standard." Liability attaches even without knowledge or intent. "The agent picked the payee" won't save you. The decision moved to software. The liability didn't.
What will the agent learn to game? This one worries me most. Tell an agent to minimize fees and friction, and the agent figures out payments under the $3,000 U.S. Travel Rule threshold move with less data. So ten payments of $2,900 instead of one of $29,000. If a human did this, we'd be opening a case. When an agent does this, the vendor calls the behavior optimization.
How do you take the authority back? Think about removing an authorized signer. The company sends a letter, the bank updates the signatory list, and the old signer is out. Now picture one agent connected to a company's bank account, corporate card and exchange account at the same time. The company drops the vendor. Who tells all three? If one of them misses the update, the old agent still holds working credentials, and the next payment goes out anyway. Granting authority to an agent takes one click. Taking the authority back has to be as fast, everywhere at once.
The part banks should worry about
Today, a business logs into the bank to pay a supplier. The bank sees the customer, the payment and the approval. The relationship lives at the bank.
With an agent, the business never logs in. The agent finds the supplier, agrees the price and sends the payment from whichever account is connected. The customer talks to the agent, not the bank. The bank still holds the money and still carries the regulatory risk, but loses the relationship.
So what keeps the bank relevant? Control. The bank sits in the right spot to check the agent's authority before money leaves the account:
- Is this agent allowed to make this payment?
- Is the amount inside the limits the customer set?
- Has the customer pulled the agent's authority?
- Is there a record of what the customer asked for and what the agent did?
- If the agent gets the payment wrong, who fixes the problem for the customer?
Compliance teams already do this kind of checking every day. With agents, those checks stop being back-office work. They become the reason customers keep banking with you.
Where the Travel Rule fits (and where the Travel Rule stops)
The Travel Rule already does half the job for virtual asset transfers. Originator and beneficiary data move with the transfer between the VASPs on each side. What the data doesn't carry yet is the mandate: who authorized the agent, for what, within which limits, and until when.
Look at IVMS101, the common data model for Travel Rule messages. There's an originator, a beneficiary, the VASPs on each side and any intermediary VASPs. There's no field for software acting on someone's behalf.
Timing matters too. On a blockchain or a shared ledger with final settlement, there's no recall. If an agent pays the wrong party at 2 a.m. on a Saturday, the money is gone before anyone wakes up. The check has to happen before settlement, not after.
And standards take a long time. The FSB's Martin Moloney noted in July ISO 20022 adoption sits around 77% of fast payment systems and 53% of settlement systems, more than two decades in. Agents won't wait twenty years for us.
This is why we built the Transaction Authorization Protocol (TAP) as an open protocol. Agents acting for each party exchange identity, authorization and settlement details before anything settles. A connect message (TAIP-15) carries the mandate itself: the principal, the agent asking for authority, allowed purposes, spending limits, approved beneficiaries and assets, and an expiry. The other side sees the authority before the money moves and not after.
At Notabene we talk about two problems: knowing who sits behind a blockchain address, and settling a payment with counterparties you know. Agents add a twist to the first one. Knowing who sits behind the address now includes knowing who speaks for them.
Even Waller pointed this way, toward standards showing what the buyer intended and how the agent carried out the instruction.
If I were back in a CCO seat
The things I'd start thinking about when it comes to an “AI Payment Agent Compliance Program” would be:
- Find the agents you already have. Ask where software, not a person, starts payments today. Look at treasury tools, invoice platforms and vendor apps, including the ones nobody calls "AI."
- Write down what each agent is allowed to do. Record who gave the permission, what the agent is allowed to pay for, the spending limits and the end date. Keep this in the customer file, next to the KYC.
- Get the same details from the other side. Before a payment settles, ask the bank or VASP on the other end which agent sent the payment and who authorized the agent. The Travel Rule and pre-transaction authorization would be a key mitigating control here. I would also spell out in your contracts who pays when an agent makes a mistake.
- Save the request and the result. Keep a record of what the customer asked for and what the agent did. When a dispute comes in, the answer sits in the difference between the two.
- Practice shutting an agent off. Turn off one agent's access and time how long until the payments stop. If the answer is hours, you have a gap to fix.
KYC tells us who the customer is. Know Your Agent has to tell us who speaks for the customer, how far the authority goes, and how to take the authority back.
If you're already seeing agent-initiated payments in production, I'd like to compare notes.
Summary and key takeaways
Most institutions have stopped asking whether to use stablecoins. The open question is how to run them safely at scale, and that is where the friction now sits.
Jack McDonald, SVP of Stablecoins at Ripple, joins Alice Nawfal, President and co-founder of Notabene, to talk through what that takes. Jack came to Ripple through its acquisition of Standard Custody & Trust, the institutional custodian he co-founded in 2018. Before that he spent more than a decade running a broker-dealer and fund administration business, so he approaches stablecoins as an operator.
His view is that the settlement infrastructure institutions need largely exists today, and that US regulation has moved from headwind to tailwind since the GENIUS Act. What remains is education and trust. Institutions need to understand what each counterparty's license means and who sits on the other side of a transaction. They also need to accept that a cross-border payment is only as good as its last-mile payout, which is where newer entrants most often underestimate the work.
Jack explains why Ripple made a strategic investment in Notabene, what changes when RLUSD runs inside Notabene Flow, and why RLUSD's daily activity matters more to him than its market cap. He also describes how Ripple is bringing 1,400 corporate treasury customers on chain, starting at the crawl stage.
He closes with a test for success: the day an operator stops switching between a TradFi screen and a digital asset screen.
Key takeaways
- The infrastructure is largely built. Jack sees three factors in institutional adoption: regulatory clarity, infrastructure, and education. Infrastructure is mostly in place, and education is now the bottleneck.
- Stablecoins are the easiest first step. Jack calls them the least controversial way for an institution to enter digital assets, helped by the GENIUS Act giving US stablecoins a federal framework.
- Institutions need to know who they are dealing with. That means understanding the licenses held by the issuer, the custodian, and the payment service provider, and verifying the counterparty on the other side of each transaction.
- The last mile decides straight-through processing. Payments into G7 banking corridors tend to run smoothly. Secondary and tertiary markets are where fragmentation shows up, and where local payout partners matter most.
- Daily activity beats market cap as a measure of utility. RLUSD's daily activity grew from about $100M at the start of 2026 to $1.3B a day by August, according to Jack, driven by payments and capital markets use.
- Success means one operating system. Jack's finish line is capital markets and payments running on one system, with stablecoins used as collateral and as a payment instrument, and nobody calling it crypto anymore.
Speakers
Jack McDonald, SVP of Stablecoins, Ripple
Jack leads Ripple's stablecoin business, including RLUSD. He joined Ripple in 2024 through its acquisition of Standard Custody & Trust, the New York-chartered institutional custodian he co-founded with Ripple co-founder Arthur Britto in 2018 and still leads as CEO. Before moving into digital assets, he spent more than a decade as CEO of Conifer Financial Services, which ran a broker-dealer, middle office, and fund administration business, and earlier worked on the sell side at UBS.
Alice Nawfal, President and co-founder, Notabene
Alice co-founded Notabene and leads its business and operations. She was previously Chief Operating Officer at uPort, the identity platform from ConsenSys built on Ethereum, and before that a management consultant at Bain & Company. She holds a public policy degree from the Harvard Kennedy School and an MBA from Wharton.
Links: Author page · LinkedIn
SAN FRANCISCO, September 17, 2026 —
Sardine, the leading agentic risk platform for fighting financial crime, today announced a partnership with Notabene, the trust layer for global money movement, to bring their industry-leading transaction authorization to Sardine's platform. Through the integration, Sardine customers can manage and automate their Travel Rule requirements and transaction authorization alongside fraud, KYC/KYB, AML transaction monitoring, and sanctions screening within a single, unified platform.
The partnership comes as regulatory clarity accelerates across the crypto and stablecoin industry with the EU’s Markets in Crypto-Assets Regulation and Transfer of Funds Regulation (MiCA/TFR), Brazil's BCB Resolution 520, and broader adoption of the Financial Action Task Force's Travel Rule standards giving companies the certainty to invest with confidence. That stability is drawing a new wave of fintechs and traditional financial institutions into the stablecoin market, and a rising demand to consolidate compliance infrastructure.
The integration pairs Notabene's transaction authorization platform, and the largest network of regulated entities in the industry, with Sardine's risk platform to provide joint customers with a single point of access to both. This allows customers to not only manage Travel Rule requirements alongside the rest of their risk and compliance operations, but also feed transaction-level decisions back into Sardine to strengthen their overall risk management posture.
"Notabene has the deepest counterparty network in the industry, and now it's integrated directly into Sardine's platform. That means our customers can handle Travel Rule compliance alongside fraud, KYC/KYB, AML monitoring, and sanctions screening all in one place, without adding another vendor to manage.”
—Soups Ranjan, CEO and Co-Founder of Sardine
“Crypto and stablecoin companies shouldn’t have to choose between transaction-level or customer-level risk. Both are critical components of a robust compliance stack. By bringing our network and transaction authorization platform together with Sardine's, joint customers get real-time counterparty verification and transaction authorization running alongside the fraud and AML tools they already rely on, in one place."
—Alice Nawfal, Co-founder and CEO of Notabene
Notabene's network connects thousands of trusted counterparties, facilitating trillions of dollars in transaction volume annually across more than 100 jurisdictions, extending the number of counterparties that customers can safely transact with, on the open-loop and ISO 20022-compatible Transaction Authorization Protocol. While Travel Rule compliance is the entry point for many of its customers, Notabene's core service is transaction authorization infrastructure, providing tools for stablecoin payment coordination, real-time transaction authorization, counterparty verification, and self-hosted wallet identification that help institutions increase their straight-through processing rates and build trust into every transaction.
Sardine backs that network with a risk platform built to help crypto and stablecoin companies detect and stop financial crime across the customer lifecycle, from onboarding and KYC/KYB through transaction monitoring and sanctions screening.
About Sardine
Sardine is the leading agentic risk platform for fighting financial crime. Our integrated fraud and AML solutions unify data across risk teams, enabling real-time fraud detection and automated compliance operations. More than 450 global enterprises rely on Sardine to secure and grow their products, including category leaders across banking, fintech, wealth and retirement, HR and payroll, payments, and software. Customers include FIS, Experian, National Bank of Canada, Nubank, GoDaddy, Deel, Gusto, Paylocity, Xero, and ZoomInfo. Learn more at sardine.ai.
About Notabene
Founded in 2020 and headquartered in New York, Notabene operates the largest open network of regulated on-chain transactions, enabling 280+ institutions — such as Ripple, Copper, Crypto.com, OKX, Boerse Stuttgart, and more — to confirm and verify counterparties in real time, authorize transactions before settlement, and unlock compliant B2B stablecoin payments. Notabene connects thousands of trusted counterparties, facilitating trillions of dollars in transaction volume annually across over 100 jurisdictions. To learn more, visit notabene.id.
Media Contacts
Aaron Berger
AM Partners (for Sardine)
917.355.8959
Clay Fain
VP, Marketing (for Notabene)
Stack Chats Episode 5: Bringing Stablecoin Payments to Latam with Andres Junge
Guest: Andres Junge, Founder, Anyenk
Host: Pelle Braendgaard, CEO & Co-Founder, Notabene
Topics: Stablecoins, Payments Infrastructure, Compliance, Interoperability, Latin America
In this episode of Stack Chats, Notabene CEO Pelle Braendgaard sits down with Andres Junge of Anyenk to discuss brining B2B stablecoin payments to Latam with Notabene Flow.
Watch the full episode below:
🎙️ Stack Chats is Notabene's video series for product leaders, fintech builders, and infrastructure innovators shaping the next generation of blockchain-based payments.

Anyenk, the Chilean company building digital-asset payment infrastructure for businesses across Latin America, has launched its native integration with Notabene Flow, the open B2B stablecoin payments network. Its customers can now invoice buyers and pay suppliers anywhere in the network in stablecoins, with the compliance and reconciliation work handled as part of the payment rather than after it.
The problem Anyenk set out to solve is familiar to any exporter in the region. A Peruvian manufacturer invoicing a buyer in Europe waits days for correspondent banking to clear and pays a fee at every stage. Moving to stablecoins fixes the speed and the cost, but settles a payment with no invoice reference, no verified sender, and nothing for the finance team to reconcile against.
Anyenk's founder and CEO, Andres Junge, co-founded Notabene in 2020 and served as its CTO through 2024, making him one of very few people who have architected payment infrastructure and then built a company that runs on it.
"I spent years building the trust layer that makes institutional digital-asset payments work. What I can see now, from the other side, is what it is worth to a manufacturer in Santiago. The same network that was built to ensure compliant digital asset transactions now enables an invoice to get paid in minutes instead of days, by a verifiable counterparty, with all of the invoice details attached so their finance team can reconcile the transaction.. That is exactly the long-term vision we had in mind when founding Notabene to bring crypto to the everyday economy, and I’m privileged to help make this a reality with the work we’re doing at Anyenk for the Latin American market."
—Andres Junge, Founder of Anyenk
On Notabene Flow, the counterparty, the chain, and asset are verified before anything settles. Travel Rule compliance data is carried securely and automatically, while the invoice reference travels with the payment, so the funds arrive ready to reconcile in the books.
One integration for Anyenk reaches counterparties held at any of the 290+ regulated institutions active on Notabene across more than 100 countries, with no bilateral relationship to negotiate per corridor.
"Latin America is where the case for compliant stablecoin payments is most obvious. Correspondent banking is expensive, and the businesses at both ends are sophisticated enough to move the moment something better exists. Anyenk is demonstrating what the Notabene network does for real trade, and there is no stronger validation of the architecture than one of its designers choosing to build his own company on it."
—Pelle Brændgaard, Co-founder of Notabene
Notabene and Anyenk are hosting a joint session on compliant stablecoin payments for Latin American businesses later in September — stay tuned for details.
To learn more about how Anyenk and Notabene can help with your B2B stablecoin payment infrastructure in Latin America, schedule time with our team.
About Anyenk
Anyenk builds digital-asset payment infrastructure for Latin American businesses, providing non-custodial institutional wallets and coordinated access to local and global fiat rails.
About Notabene
Notabene is the compliance and authorization layer for institutional digital-asset payments. Its network connects 290+ regulated institutions across more than 100 countries, reaches over 2,300 institutions, and has processed more than $2.5 trillion in transactions. Notabene Flow is its open B2B payments network, allowing companies to send and receive compliant stablecoin payments on the world’s largest network of regulated institutions.
We've designed a new analytics experience in Transact, built to show you how much of your transaction flow is clearing without human hands on it.
Most analytics products are designed for the quarterly review. Someone opens them once, exports a chart into a board deck, and closes the tab for six weeks.
That is not how compliance teams work.
So we designed against a different test. A compliance officer logs in at 8am with coffee. They glance at the status breakdown to see if anything stalled overnight. They check outstanding due diligence requests. They look at volume week over week. They scan top counterparties. They check what percentage resolved automatically. Then they close the tab and get on with the day.
Ninety seconds, start to finish.
If the dashboard supports that ritual, we built the right thing. If it takes five minutes to find any one of those answers, we didn't. Everything below follows from that.
Transaction Metrics
The first of two views. It answers the question you have before you've finished your coffee: is anything wrong, and how much did we have to touch by hand?
Percent resolved automatically is the number most teams end up watching hardest, because it is your straight-through processing rate made visible. Every transaction that clears without a person opening it is time your team didn't spend, and cost your business didn't carry. Watching that number is how you find out whether your policy configuration is doing its job or whether your team is quietly absorbing work that automation should be handling. When it dips, a policy usually needs attention. When you tune one and it climbs, you can see the return.
That has always been the point of configurable authorization workflows. Until now you had to infer the effect. Now you can watch it.
Status breakdown shows where your transactions actually sat, so a pile-up in one state is visible immediately rather than at month-end.
Median response latency tells you how long counterparties actually take to come back to you. Median rather than mean, deliberately: a handful of outliers shouldn't distort your view of a normal day. Slow counterparties are one of the largest drags on straight-through processing, and this is where you find out which ones they are.
Hosted vs self-hosted splits, broken out by proof of ownership type, show the shape of your self-hosted wallet exposure. Given where supervisory attention is going, this is a view worth knowing before someone asks you for it.
Counterparty Metrics
The second view is about who you're transacting with.
Active counterparties and top counterparties by volume show concentration. Most teams have a rough sense of their largest relationships. The ranked view tends to surprise people anyway.
Top jurisdictions does the same for geography, which matters more each quarter as obligations activate in new markets on different timelines.
Due diligence status is the one we're most pleased with, because it doesn't dead-end. Every counterparty's DD status links straight through to DD Management. You spot the gap and you act on it in the same motion, rather than noting it somewhere and coming back later. Incomplete due diligence is a common reason transactions fall out of automation, so closing those gaps feeds directly back into the number at the top of the page.
The global transaction flow map
An interactive map of your transaction flows, showing where value is actually moving across your network.
It is the fastest way to explain your business to someone who doesn't live in it. Auditors, boards, and new team members understand a map immediately, in a way they don't understand a table.
Export when you need it
CSV export is included throughout. The dashboard is built for the daily glance, but reporting season is real, and your data should come with you when it arrives.
Where to find it
Look for Analytics in the left-hand menu. It's rolling out now, with no configuration required.
Book a walkthrough with your customer success manager or schedule a demo with the team
This guide explains what the Notabene Flow MCP server is, how to connect it to Claude and Codex clients—claude.ai in the browser, Claude Desktop, Claude Code, Codex desktop, and Codex CLI—and how to use its tools once connected.
What is the Notabene Flow MCP server?
MCP (Model Context Protocol) is the open standard that lets AI assistants such as Claude and Codex call tools on external services. Notabene Flow provides a hosted MCP server that brings compliant stablecoin payment link generation directly into your AI assistant.
In practice, that means you can hand your assistant an invoice—a PDF, an image, pasted text, or just a description—and ask it to “create a payment link for this.” The assistant extracts the invoice data, helps you choose where the funds should settle, and creates a payment link you can share with your customer, with Notabene handling Travel Rule compliance behind the scenes.
Key properties:
- The assistant acts for the merchant—the business getting paid. Your identity is your verified login email; it is never something the assistant or an uploaded invoice can override.
- Login is simple. Connecting from any supported client opens a login page where you enter your email and a one-time code sent to it. Sessions last up to 7 days, then you sign in again.
- Interactive previews. On ChatGPT, claude.ai and Claude Desktop, previewing or creating an invoice renders a live invoice preview in the conversation. CLI clients return equivalent text summaries instead.
Endpoint
https://flow.link/mcp
Authentication endpoints are discovered automatically—this is the only URL you enter.
Connecting
Claude (web)
- Click your initials in the lower-left corner, then select Customize → Connectors.
- Click Add → Add custom connector.
- Enter
https://flow.link/mcpand click Add. No OAuth client ID or secret is needed. - Click Connect. Enter your email in the Notabene Flow login, then the one-time code sent to it.
- In a chat, click the + button, open Connectors, and make sure the connector is enabled.
On Team and Enterprise plans, an organization admin adds the connector first under Admin settings → Connectors. Members then connect with their own email from Customize → Connectors.
Claude Desktop app
Open Customize → Connectors → Add → Add custom connector, enter https://flow.link/mcp, then click Connect and complete the email login. Enable it in a conversation through the + → Connectors menu.
Claude Desktop supports the interactive invoice preview, so previews and created payment links render inline in the conversation.
Claude Code (CLI)
Add the server over HTTP transport:
claude mcp add --transport http notabene-flow https://flow.link/mcp
Use --scope user to make it available in all your projects, or --scope project to write it to a shareable .mcp.jsonfor your team.
Inside a session, run /mcp, select the server, and choose Authenticate. Your browser opens the Notabene Flow login. claude mcp list shows the connection status.
Claude Code does not render the interactive preview; the tools return text summaries instead.
ChatGPT/Codex desktop app
- Open the Plugins page.
- Click Add in the upper-right corner, then select Add MCP server.
- Enter
notabene-flowas the name andhttps://flow.link/mcpas the server URL. - Complete the form to add the server.
- When prompted, complete the Notabene Flow login using your email and the one-time code sent to it.
- Open the MCPs tab on the Plugins page to check that Notabene Flow is connected.
Once connected, try: “Use Notabene Flow to list the supported settlement assets and chains.” Then provide an invoice and ask Codex to validate and preview it before creating a payment link.
Codex CLI
Register the server and sign in from your terminal:
codex mcp add notabene-flow --url https://flow.link/mcpcodex mcp login notabene-flow
Complete the Notabene Flow email login in your browser. Run codex mcp list to inspect the configuration, then start Codex and run /mcp to check the active connection.
Codex desktop and Codex CLI share MCP configuration on the same host, so setup in either client is sufficient. Restart an already-running client after adding the server.
Codex CLI does not render the interactive invoice preview. Ask it to use preview_invoice_text, then review the invoice and settlement destination before requesting the payment link.
Using the tools
Available tools
update_profile— Sets your merchant display name and optional tax ID or address shown on every payment link.get_invoice_extraction_guide— Gives the assistant the extraction guide to follow when you upload or paste an invoice.validate_invoice— Normalizes and validates an invoice without creating anything.preview_invoice/preview_invoice_text— Shows the invoice before committing, as an interactive preview in supported clients or as text in CLI clients.list_supported_assets— Lists the stablecoin assets and chains a payment link can settle in.find_provider— Looks up an exchange or custodian such as Kraken, Coinbase, or Fireblocks.request_wallet_proof— Creates a single-use, 24-hour signing link for proving ownership of a self-hosted wallet. No funds move.get_wallet_proof_status— Checks a wallet-proof request and returns the settlement address once signed.create_invoice_payment_link— Issues the payment link.
Typical flow
- Set your profile once: the assistant calls
update_profilewith your business display name. - Get the invoice in: upload or paste an invoice, or describe it. Your customer’s email is required so the payer is identifiable.
- Preview: the assistant validates and previews the invoice so you can confirm it before committing.
- Choose the settlement wallet where funds land. Use a wallet from a previous invoice, an account at an exchange or custodian found with
find_provider, or a new self-hosted wallet verified throughrequest_wallet_proof. - Create the link:
create_invoice_payment_linkreturns the payment link URL. Share it with your customer, who opens it, picks an asset and chain, and pays. You are shown as the beneficiary.
Example prompts once connected:
“Here’s an invoice PDF—create a payment link for it. Settle to my Kraken account.”
“Create a $500 payment link for consulting services for [email protected], settled to the wallet I used last time.”
Good to know
- After you sign a wallet proof, it can take up to a minute for the signature to appear. The assistant will wait and re-check.
- Wallet ownership proofs are per wallet, not per invoice: sign once, and later invoices skip the step.
- An optional bank account adds a fiat payment fallback to the link.
- Payment links are valid for 60 days by default. If the invoice has a due date, the link stays payable until 60 days after it, capped at 2 years from creation. Wallet-proof signing links are single-use and expire after 24 hours.
- Travel Rule compliance is handled by Notabene. A new self-hosted wallet needs a signed ownership proof before it can receive a link.
Notabene Announces Strategic Investment from Ripple
Ripple invests in the trust infrastructure needed to scale stablecoin payments
NEW YORK — Notabene, the operator of the world’s largest open network for regulated on-chain transactions, today announced a strategic investment from Ripple, the leading provider of blockchain-based enterprise solutions across traditional and digital finance.
Alongside the investment, Notabene and Ripple will collaborate to expand enterprise stablecoin payments by integrating Ripple USD (RLUSD) into Notabene Flow and exploring how trusted payment authorization can complement Ripple Payments. Notabene Flow is Notabene’s B2B stablecoin payments platform that enables payment coordination and authorization capabilities, which leverage and are built on top of Notabene’s scaled transaction authorization network. By combining Ripple’s global enterprise ecosystem and RLUSD stablecoin with Notabene’s trusted institutional network, which today facilitates over $2 trillion in annualized transaction volume, the partnership is set to accelerate adoption of compliant stablecoin payments while creating a pathway for RLUSD to be integrated across one of the world’s largest institutional payment networks for digital assets. Together, the companies aim to make compliant stablecoin transactions easier for financial institutions to adopt at scale.
To date, Notabene has built the largest open network for moving value on-chain safely, combining Travel Rule compliance with broader pre-transaction verification and authorization capabilities. The network spans more than 2,300 connected institutions, 100+ global jurisdictions, and 280+ customers, including tier-1 banks, custodians, fintechs, and global exchanges, and has facilitated over $2 trillion in annualized transaction volume. Through Notabene Flow, the company is extending its trust network and infrastructure into novel capabilities for B2B and agentic stablecoin transactions, including pull payments, recurring payments, and automated invoicing solutions.
As financial institutions move from experimentation to production with stablecoins, institutions need to know who they are transacting with, verify counterparties and transaction details before value moves, and meet regulatory and internal risk requirements without introducing friction. Notabene's trust network helps solve that challenge, making it a natural complement to Ripple’s enterprise payments and stablecoin infrastructure.
“Stablecoins are quickly becoming part of mainstream financial infrastructure, but institutional adoption depends on more than efficient settlement rails alone. It requires trusted identity, compliance, and transaction authorization before value moves. Notabene’s network addresses one of the fundamental barriers to enterprise adoption, and together we're helping build the compliant infrastructure institutions need to move value at global scale while expanding the utility of RLUSD.”
Jack McDonald, SVP of Stablecoin at Ripple
Ripple’s investment comes amid growing demand for regulated digital asset infrastructure, as banks, payment networks, fintechs, and new stablecoin consortia move to launch tokenized cash products and embed stablecoin rails into their existing offerings. Institutional momentum in adopting digital assets as core financial infrastructure has been reinforced by growing regulatory clarity globally, including the passage of the GENIUS Act in the United States and MiCA in the European Union. As stablecoins become increasingly utilized in regulated, high-value flows, institutions must verify counterparties and authorize transactions before value moves—capabilities that sit at the core of Notabene’s platform.
“Every institution I talk to has moved past whether to use stablecoins. They are stuck on how to do it safely at scale within the context of their existing business. They need to know who is on the other side, what the transaction is for, and how to authorize payments without adding friction. That is what Notabene and its network of regulated institutions solve. Paired with an enterprise-ready stablecoin like RLUSD and Ripple’s global payments reach, it turns compliant stablecoin payments from a pilot into a real growth engine that reaches more counterparties and moves more volume, faster,”
Pelle Braendgaard, Co-Founder and CEO of Notabene
With the investment, Notabene will leverage Ripple’s enterprise ecosystem to accelerate the rollout of Notabene Flow, extending compliant stablecoin payments to institutions worldwide.
Establishing strategic partnerships is a core pillar of Notabene's strategy for scaling Notabene Flow, and it expects to bring on other leading financial institutions over the coming quarters.
About Notabene
Founded in 2020 and headquartered in New York, Notabene operates the largest open network of regulated on-chain transactions, enabling institutions to confirm and verify counterparties in real time, authorize transactions before settlement, and unlock compliant B2B stablecoin payments. Notabene serves 280+ customers across global banks, fintechs, custodians, and exchanges. To learn more, visit notabene.id.
About Ripple
Founded in 2012, Ripple is the leading provider of blockchain-based enterprise solutions across traditional and digital finance. Its solutions span global payments, custody, liquidity, and treasury management, serving as a one-stop shop for moving, storing, exchanging, and managing value. Ripple’s stablecoin, RLUSD, and the cryptocurrency XRP underpinning these solutions allow Ripple and its customers to shape the modern financial system.
Media Contacts
Notabene Media Contact: Clay Fain, VP of Marketing <[email protected]>
Ripple Media Contact: Amy Dunn, Product Communications <[email protected]>
The FATF's seventh Targeted Update shows Travel Rule laws in place across 93% of surveyed jurisdictions. The gap now is enforcement.
Eight years after the FATF extended its AML/CFT Standards to virtual assets, the annual check-in on the progress has arrived. On 15 July 2026, the FATF published its seventh Targeted Update on Implementation of the FATF Standards on Virtual Assets (VAs) and Virtual Asset Service Providers (VASPs), drawing on survey responses from 147 jurisdictions, 149 mutual evaluations and follow-up reports, and a year of Virtual Assets Contact Group work, including the December 2025 symposium.
The report’s headline figure is clear: 83% (91 of 109) of surveyed jurisdictions now have Travel Rule legislation in force, up from 73% last year. When adding in the 11 jurisdictions with legislation in progress, 93% (102 of 109) of surveyed jurisdictions have Travel Rule either in force or in progress, compared with a combined 85% in 2025.
For years, the sunrise issue was cited as a major compliance barrier: firms subject to the Travel Rule often struggled to comply when transacting with counterparties in jurisdictions where equivalent obligations did not yet apply, leaving compliant firms to absorb the operational burden and cost. The latest data shows that this legislative adoption gap is now closing. Travel Rule laws are largely in place; the more persistent challenge is no longer adoption, but effective supervision and enforcement.
Here are our takeaways.
1. The Travel Rule question changed from "is there a law" to "does anyone check"
Of the 91 jurisdictions with Travel Rule legislation in force, 55 (or 60%) have not issued a single finding, directive, or enforcement action on Travel Rule compliance. The FATF partially attributes this gap to timing, noting that many of the laws are recent and supervisory frameworks are still being established. It also directs supervisors to its 2025 Best Practices in Travel Rule Supervision paper.
Yet, the report cautions that persistent gaps in Travel Rule implementation remain a serious concern, and jurisdictions with the rule on the books should rapidly operationalize supervision and enforcement.
Notabene's commentary:
The sunrise issue is entering a second phase. The original problem was counterparties with no legal obligation to comply. The new one is counterparties with a legal obligation, and nobody is checking whether they meet it. From the perspective of a compliance officer of a compliant firm, the two look identical: incomplete data, unanswered transfers, and costs concentrated on the firms taking the rule seriously.
Our advice to VASPs has not changed. Build to the rule, not to the enforcement posture. Enforcement shows up unevenly, without much warning, and sometimes through channels nobody planned for. Firms waiting for the first knock end up remediating under pressure instead of complying on their own schedule.
2. R15 Technical Compliance Is Improving—But Slowly
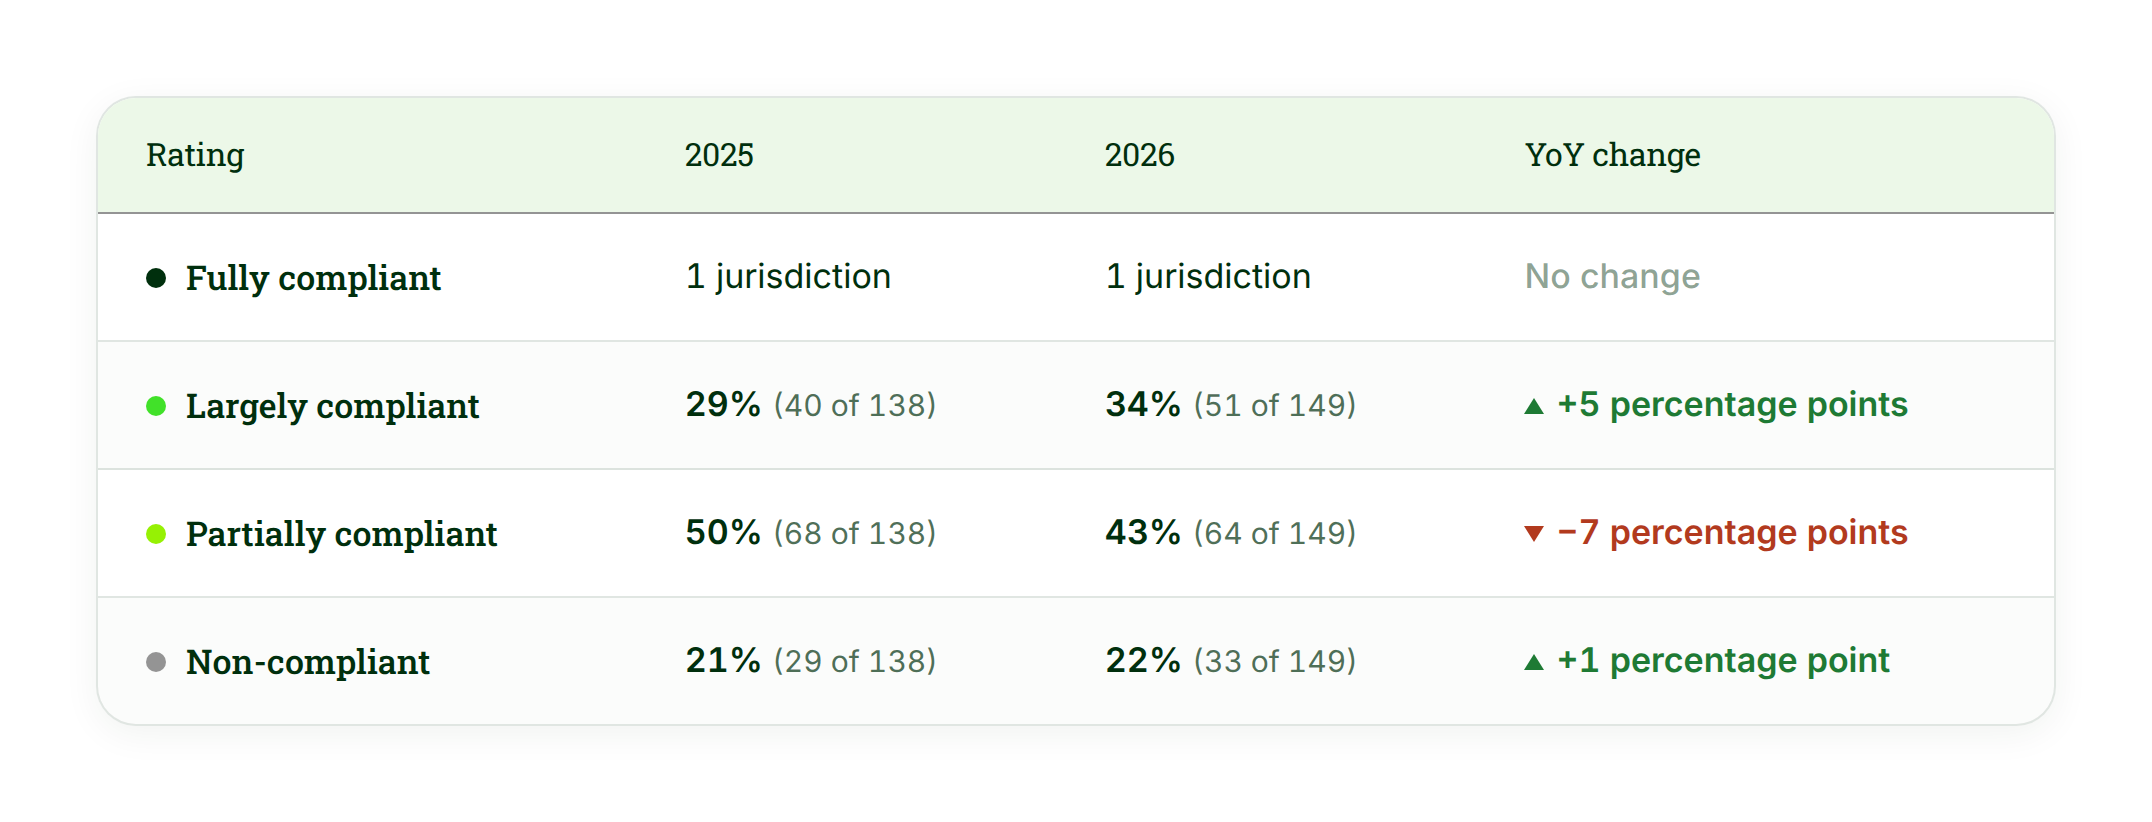
Technical compliance with FATF Recommendation 15 improved modestly in 2026. One jurisdiction was rated fully compliant in both 2025 and 2026. The share rated largely compliant increased from 29% in 2025 to 34% in 2026, while the share rated partially compliant fell from 50% to 43%. The proportion rated non-compliant remained broadly unchanged, rising slightly from 21% to 22%. Overall, the results point to gradual progress, but nearly two-thirds of assessed jurisdictions remain only partially compliant or non-compliant.
Notabene's commentary:
The increase in largely compliant jurisdictions is encouraging, but the fact that nearly two-thirds remain only partially compliant or non-compliant shows that uneven regulatory maturity will continue to create operational complexity for VASPs. Firms still need to manage inconsistent requirements, supervisory expectations, and counterparty readiness across markets. In practice, technical compliance scores are improving, but the cross-border compliance environment remains fragmented.
3. Risk assessments are being written, not used
86% of jurisdictions (124 of 145) report having conducted an ML/TF/PF risk assessment covering VAs and VASPs, up from 76% in 2025. However, the mutual evaluation results tell a different story: Only 48 of 149 (32%) assessed jurisdictions were found to meet or mostly meet the criteria that assess whether preventive and/or mitigation measures are implemented in line with the identified risks.
Notabene's commentary:
A document is not a control. Where implementation stalls is the distance between writing a risk assessment and using one to steer supervisory resources. FATF has flagged this same pattern across several consecutive updates. For jurisdictions looking for a place to start, the report points to the December 2025 VACG symposium materials and to a VA/VASP annex to the ML National Risk Assessment Guidance, expected later in 2026 (para. 11).
4. Prohibition of VA activities more than doubled since 2023
The share of jurisdictions prohibiting VASPs has risen steadily over the past four years, more than doubling from 11% in 2023 to 23% in the latest survey.
Although prohibition is permitted under the FATF Standards, it does not remove the need for active oversight. Jurisdictions must still identify prohibited virtual asset activity, detect VASPs operating illegally, and take appropriate supervisory or enforcement action. Without that capacity, a prohibition may simply push activity outside the regulated perimeter rather than eliminate it.
There are signs, however, that jurisdictions adopting prohibitions are becoming more active in enforcing them. In the latest survey, 16 of the 21 jurisdictions explicitly prohibiting VAs and VASPs reported taking supervisory or enforcement action against operators acting illegally—approximately 76%. That compares with 9 of 17 jurisdictions, or 53%, in 2025. The increase indicates that prohibition regimes are becoming more operational, although their effectiveness still depends on whether authorities can consistently identify and sanction activity taking place outside the legal perimeter.

Notabene's commentary:
A prohibition nobody enforces is an unregulated market. Transactions keep flowing, no entity holds a license, and no Travel Rule data moves. For VASPs in permitting jurisdictions, this creates a quiet exposure: inbound flows from prohibited markets arrive with no compliant counterparty on the other side. Risk teams should treat prohibition jurisdictions as a distinct counterparty class, not an empty set.
5. Criminals are now building infrastructure because compliance is working
The report's most telling case study involves a Cambodia-based financial services conglomerate found to have laundered at least USD 4 billion between August 2021 and January 2025, including at least USD 37 million tied to DPRK cyber heists funding weapons programs.
A third-party stablecoin issuer froze more than USD 29 million in a wallet linked to the group. The group's response was to issue its own USD-pegged stablecoin, marketed as immune to freezing and deployed across multiple public blockchains plus a proprietary chain.
The freeze worked. Issuer-level controls did exactly what they were designed to do, and the criminals left the regulated asset entirely.
Notabene's commentary:
Two things worth noting. First, compliance controls shape criminal behavior, which is the whole point of having them. Second, the FATF now says openly what this case implies: obligated entities should not lean on issuer-level freeze and burn capability as a universal safeguard, because the highest-risk assets are increasingly issued by parties outside any oversight. Where the issuer is the adversary, controls have to live at the transaction and counterparty level.
The same section documents ISIL and Al-Qaeda shifting from Bitcoin toward stablecoins, paired with rotating wallet addresses, micro-split transfers, and OTC brokers with minimal customer due diligence. Stablecoin misuse is no longer an "emerging risk" in FATF language. This is a documented typology with named actors.
6. The regulatory perimeter is shifting from incorporation to activity
Offshore VASPs remain, in the FATF's words, a significant challenge. 39 of 114 jurisdictions with licensing frameworks (34%) now extend licensing or registration to offshore VASPs based on activity anchors: targeted marketing, onboarding of residents, and use of domestic payment rails. Some go further and require a local compliance officer with unrestricted access to customer data and enough seniority to act independently.
The report also walks through nested arrangements in which offshore VASPs open accounts on licensed platforms, posing as retail users, then push through illicit volumes far beyond anything retail. The FATF's private sector recommendations answer this directly: enhanced due diligence on offshore VASPs, detection of misrepresented accounts, restricting or exiting higher-risk relationships, and monitoring fiat on-ramp and off-ramp activity linked to weakly supervised platforms.
Notabene's commentary:
Activity-based licensing is expanding the regulatory perimeter beyond where a VASP is incorporated to where and how it operates. The nested VASP typology places a corresponding burden on regulated platforms: the risk may sit inside a customer account that is presented as retail but is, in practice, being used to provide virtual asset services at scale. Firms need controls capable of identifying when account behavior, transaction volumes, and payment flows are inconsistent with the stated profile.
7. DeFi Oversight Remains at an Early Stage
The 2026 survey points to limited regulatory engagement with DeFi. Only 18% of responding jurisdictions have assessed DeFi-related risks, while a further 9% are in the process of doing so. At the same time, 93% have not identified any DeFi arrangements operating in their territory that would qualify as VASPs under the FATF Standards. Although 31% reported that their existing risk-mitigation measures apply to DeFi arrangements, implementation remains rare: only four jurisdictions have imposed licensing or registration requirements, and just two have licensed or registered a DeFi arrangement in practice. Overall, the data suggests that most jurisdictions remain at an early stage of identifying, assessing, and supervising DeFi-related activity.

Notabene’s commentary:
Regulatory uncertainty around DeFi is not merely a product of technological complexity; it reflects limited assessment and policy implementation at the jurisdictional level. 82% percent of jurisdictions have not completed an assessment of DeFi-related risks, and 69% have not applied risk-mitigation measures to DeFi arrangements. For regulated firms, this creates uncertainty over which arrangements authorities may classify as VASPs and what obligations apply when interacting with them. Until more jurisdictions take a clear stance, firms will need to manage DeFi exposure against an uneven and still-developing compliance landscape.
8. Inside the annex: what the data from 69 materially important jurisdictions shows
Annex A tracks every FATF member plus jurisdictions with materially important VASP activity, defined as trading volume above 0.25 % of the global total or a top 30 ranking by VA ownership and adoption. Together, these 69 jurisdictions handle roughly 97% of the global VA market. The table is therefore a useful snapshot of implementation across the markets that matter most, but FATF is explicit that it is based largely on self-reported information and is not, by itself, an assessment of either illicit-finance risk or effective compliance.
On paper, implementation is advanced. Excluding the six jurisdictions that fully prohibit VASP activity, 39 of the remaining 63 report completing every applicable step tracked in the annex: conducting a risk assessment, establishing a licensing framework, bringing qualifying stablecoin issuers within scope, conducting or planning inspections, taking supervisory or enforcement action, and enacting the Travel Rule. Yet these self-reported milestones do not consistently align with FATF ratings. Several jurisdictions reporting a nearly complete framework remain rated Partially Compliant or Non-Compliant, illustrating the distinction between having the formal components of a regime and implementing them to the standard tested through a mutual evaluation.
However, the ratings also need to be read with caution because they do not all describe the same point in time. Six jurisdictions in the annex—Greece, Panama, Portugal, the Republic of Korea, Saudi Arabia, and Spain—have not been assessed against the revised Recommendation 15. Among the 63 jurisdictions with a rating, 31 were last assessed in 2022 or earlier. FATF itself warns that these ratings may not reflect developments reported in the 2026 survey. A recent self-reported reform can therefore sit beside an older weak rating without either data point necessarily being wrong. Belgium illustrates this mismatch particularly clearly. It reports a risk assessment, licensing rules, stablecoin coverage, inspections, and an enacted Travel Rule, but no enforcement action—and holds a 2025 Non-Compliant rating.
The data from materially important virtual asset markets closely mirrors the broader survey findings: Travel Rule adoption is now approaching near-universal coverage. Among the 63 jurisdictions that do not fully prohibit VASP activity, 55 (87%) have enacted the Travel Rule and a further four are in progress, bringing enacted or pending coverage to 94%. This is broadly consistent with the overall survey result, where 94% of responding jurisdictions had Travel Rule legislation either in force or under development, reinforcing that the legislative sunrise gap is closing both globally and across the markets that account for the vast majority of virtual asset activity. Only Argentina, Cambodia, Colombia, and Vietnam report neither an enacted nor an in-progress Travel Rule framework.
The table also shows that different parts of the regulatory perimeter are developing at different speeds. Eleven jurisdictions report that they do not require stablecoin issuers to be licensed or registered when they qualify as VASPs under the FATF Standards. Eight of those jurisdictions already have the Travel Rule in force. This means transaction-transparency obligations may be established even where the treatment of qualifying stablecoin issuers remains incomplete. It is an important qualification to the broader implementation story: Travel Rule adoption is approaching universality in major markets, but adjacent licensing frameworks have not advanced in lockstep.
Notabene's commentary:
The annex shows that the main compliance challenge is shifting. Across jurisdictions representing 97% of the virtual asset market, the Travel Rule legislative gap is close to being resolved: 94% of jurisdictions that permit at least some VASP activity have rules either enacted or in progress. The next differentiators are whether those rules are operational, how supervisors interpret and enforce them, and whether adjacent parts of the regulatory perimeter—including stablecoin issuers licensing and offshore VASPs—are treated consistently. For compliance teams, the annex is a valuable starting point for jurisdictional risk analysis.
Where this leaves the industry
Seven updates in, the direction is clear. The standards are established and legislative adoption is accelerating. The remaining constraint is operational: effective supervision, consistent enforcement, reliable identification of both customers and counterparties, and a more level cross-border compliance environment.
For compliance teams, the report points to a practical agenda. Firms should strengthen monitoring of higher-risk unhosted wallet activity, apply enhanced due diligence to offshore VASPs, detect accounts being used to conceal nested VASP activity, assess exposure to DeFi protocols, bridges, mixers, and cross-chain tools, and treat counterparty reachability as a core control rather than a network metric.
Strong internal controls are necessary, but they are not sufficient. Travel Rule compliance is inherently bilateral: a transfer can only be completed compliantly when the institution on the other side can be identified, reached, and trusted to exchange the required information. FATF’s data shows that the legislative gap is closing, but supervisory maturity and operational readiness remain uneven. The next phase of implementation will therefore be defined less by whether jurisdictions have rules on the books, and more by whether those rules contribute to a level playing field that reduces friction in cross-border value movement.
Source: FATF (2026), Targeted Update on Implementation of the FATF Standards on Virtual Assets/VASPs, FATF, Paris.
Peru does not get enough attention in crypto compliance circles yet, the numbers argue otherwise. Close to 28 billion dollars in crypto changes hands there every year, and 9 of every 10 of those moves are dollar stablecoins people use for savings, remittances, and getting paid across borders. About 4.5 million Peruvians hold crypto. In 2025, transfers between banks and wallet services crossed 540 million, more than double the year before.
Hence, firms must pay close attention when Peru establishes a compliance timeline. The mandate is the Travel Rule, and the critical date is August 1, 2026.
The Superintendency of Banking, Insurance and Pension Funds, (“SBS”), runs AML supervision through its Financial Intelligence Unit, the UIF-Perú. In July 2024 the SBS published Resolution 02648-2024, the AML/CFT norm for Virtual Asset Service Providers, or PSAV in Spanish. Almost all of the norm went live the day after publication. One piece did not. Chapter VIII, the Regla de Viaje, got a two-year grace period, and the grace period ends this August.
Who has to comply
Any VASP domiciled or incorporated in Peru, plus Peru branches of foreign firms. The covered activities track FATF Recommendation 15: swapping crypto for cash, swapping one crypto for another, moving crypto, holding or managing crypto for someone else, and helping sell a new asset. If you do any of these for Peruvian users, you have to register with the UIF-Perú and stand up an AML program, as well as have a named compliance officer.
Registration is the only status Peru asks for right now. There is no crypto license, no capital regime, no market-conduct rulebook. A broader market law, the Ley Marco for crypto, would create an exchange register called the RUPIC, and Congress kicked the draft back to committee in March 2025. Until the law changes, the AML regime and Chapter VIII are what binds you today.
What Chapter VIII asks for
Peru treats every crypto transfer as an electronic transfer, domestic or cross-border, held to the same minimum data. The duty sits with both sides. The sending VASP and the receiving VASP each have to obtain, keep, and pass along originator and beneficiary details.
There is no de minimis exemption. Peru applies the rule to transfers of any size. What changes with size is how much you collect. Under 1,000 dollars, a lighter data set. At or above 1,000 dollars, you add the originator's address, date and place of birth, or a transaction ID.
The originating VASP has to send the data to the beneficiary VASP immediately and securely, which Peru defines as before, with, or alongside the transfer, and with the data kept intact and available. Authorities will request the same information later, and you must be ready to produce records on demand.
Self-hosted wallets are where a lot of programs get nervous, and Peru does not ban them outright. For a transfer to or from a self-hosted wallet, you collect your own customer's information and ask the customer for the counterparty's details, at the same level the table sets out.
Peru is not an outlier
This is the same FATF Recommendation 16 story playing out across Latin America, where Peru now ranks among the six largest crypto markets in the region. Stablecoins take off, transfer volume climbs, and a Travel Rule deadline follows. Peru gave two years of runway, then wrote a 120-day setup window into the resolution once the rule goes live, so real preparation time is tighter than August 1 suggests.
Where to start
Start from a clear picture of the rule. Our Peru jurisdiction page sets out the full Chapter VIII requirements, the data thresholds, and the self-hosted wallet handling in one place, and we keep the page current as the August start approaches. Use the page to brief your compliance team and product leads, then bring the counterparty and workflow questions to us.
Where Notabene fits
If you serve Peru, this is the problem we work on every day. Notabene Transact collects and checks originator and beneficiary data, lets you set policy per jurisdiction through a rules engine, and handles self-hosted wallet verification the way Resolution 02648-2024 expects.
Want to pressure-test your Peru readiness before August? Talk to our team.
What we asked FinCEN to do, and why open compliance infrastructure is the strategic prize.
The AML/CFT Programs Rule is the most consequential installment yet in FinCEN's multi-year effort to modernize the Bank Secrecy Act under the AML Act of 2020. The rule (Docket FINCEN-2026-0034) will reshape how U.S. financial institutions design and supervise their compliance programs for the next decade. Comments closed June 9, 2026.
The rule does several things:
- Codifies the AML Act of 2020’s risk-based, effectiveness-focused mandate into program requirements.
- Introduces a new supervisory and enforcement framework at proposed 31 CFR 1020.221, giving the FinCEN Director discretion to consider an institution’s innovative compliance activities and demonstrable outputs when deciding supervisory action.
- Adopts five risk assessment categories every covered institution will evaluate against.
- Sets a 12-month effective date once a final rule publishes.
The most consequential piece for digital assets is in the Supervision and Enforcement section in Question 28 “FinCEN welcomes comment on provisions related to the use of innovative tools to achieve effective outcomes, specifically on how the Director may consider the performance of innovative activities that produce demonstrable outputs under the proposed supervision and enforcement framework.”. Basically, FinCEN built a new framework for recognizing innovative compliance activities under supervision, and asked the market what counts. The answer determines whether the technology stack getting supervisory credit a decade from now is built on open standards or on proprietary vendor platforms.
We made three asks.
01. Bring back the outcomes-based effectiveness definition.
The 2020 Effectiveness ANPRM proposed defining an effective AML program as one giving law enforcement timely, useful information the government uses. Thus, outcomes and not box-checking.
The current NPRM softens the language. We asked FinCEN to restore the 2020 definition. Without an outcomes anchor, examiners default to checklists, and the new innovation framework has nothing substantive to anchor against.
02. Recognize Travel Rule infrastructure as a preventive AML control.
Question 28 asks which compliance activities deserve formal recognition as innovative. Our answer contained five things:
- Travel Rule infrastructure. Pre-settlement data exchange enabling block, freeze, and reject decisions.
- Pre-transaction authorization including the Transaction Authorization Protocol (TAP). Authorization before settlement, rather than monitoring after.
- IVMS 101 data standardization. Common counterparty data structure across institutions.
- Counterparty due diligence interoperability. GDF VASP Due Diligence Questionnaire as the shared baseline.
- Counterparty-assisted false-positive resolution. Bilateral information exchange resolving sanctions screening hits.
All five are common and open compliance infrastructure. Open standards, implementable by any party. Not proprietary single-vendor networks.
Travel Rule deserves a closer look. Most AML controls are detective and after the fact. Travel Rule, on the other hand, is preventive. Data exchange happens before settlement, which means the receiving institution blocks, freezes, or rejects a transfer before funds move on-chain.
03. Clarify the boundary between this rule and the PPSI rule.
This rule defines “distribution channels” narrowly: the methods institutions use to open accounts and deliver products. Remote onboarding, non-face-to-face channels, mobile, and similar.
A different FinCEN rulemaking already in progress, on permitted payment stablecoin issuers (Docket FINCEN-2026-0100), uses the same term much more broadly. Under the PPSI rule, blockchains themselves count as distribution channels.
Same term, two very different scopes. If institutions covered by both rules read the term the same way in their risk assessments, they end up running duplicate compliance frameworks against the same underlying risk. We asked FinCEN to clarify the boundary in the final rule.
What happens next
Twelve months after FinCEN finalizes this rule, every covered institution will be measured against a new supervisory framework. The institutions building on common and open compliance infrastructure now will have the evidence FinCEN says it wants to see. The institutions still on proprietary stacks will need a different story.
You can read Notabene's full response here: https://notabene.id/reports/notabene-response-to-fincen-aml-cft-program-nprm-fincen-2026-0034